

IBM security researchers recently announced the discovery of a new malware family called "ZeroClear ," created by the Iranian hacking group APT34 in conjunction with xHunt . This malware targets the industrial and energy sectors in the Middle East. The researchers did not disclose the names of the victim companies but published a detailed 28-page report analyzing the malware .
ZeroClear only affects Windows because, as its name describes, the program database path (PDB) of its binary file is used to execute a destructive attack that overwrites the master boot record (MBR) and partitions on compromised Windows machines.
ZeroClear is categorized as malware with behavior somewhat similar to that of “Shamoon” (malware that was widely discussed because it was used for attacks on oil companies dating back to 2012). Although Shamoon and ZeroClear have similar capabilities and behaviors, researchers say the two are separate and distinct pieces of malware.
Like the Shamoon malware, ZeroClear also uses a legitimate hard drive controller called “RawDisk by ElDos” to overwrite the master boot record (MBR) and disk partitions of targeted computers running Windows.
Although the ElDos driver is not signed, the malware manages to execute it by loading a vulnerable but unsigned VirtualBox driver , exploiting it to bypass the signature verification mechanism and load the unsigned ElDos driver.
This malware is deployed through brute-force attacks to gain access to weakly secured network systems. Once attackers infect the target device, they spread the malware across the company network as the final step in the infection process.
“The ZeroCleare cleaner is part of the final stage of the overall attack. It is designed to deploy two different forms, adapted to 32-bit and 64-bit systems.
The general flow of events on 64-bit machines includes using a vulnerable signed driver and then exploiting it on the target device to allow ZeroCleare to bypass the Windows hardware abstraction layer and bypass some operating system safeguards that prevent the Unsigned drivers run on 64-bit machines', reads the IBM report.
The first controller in this chain is called soy.exe and is a modified version of the Turla driver loader.
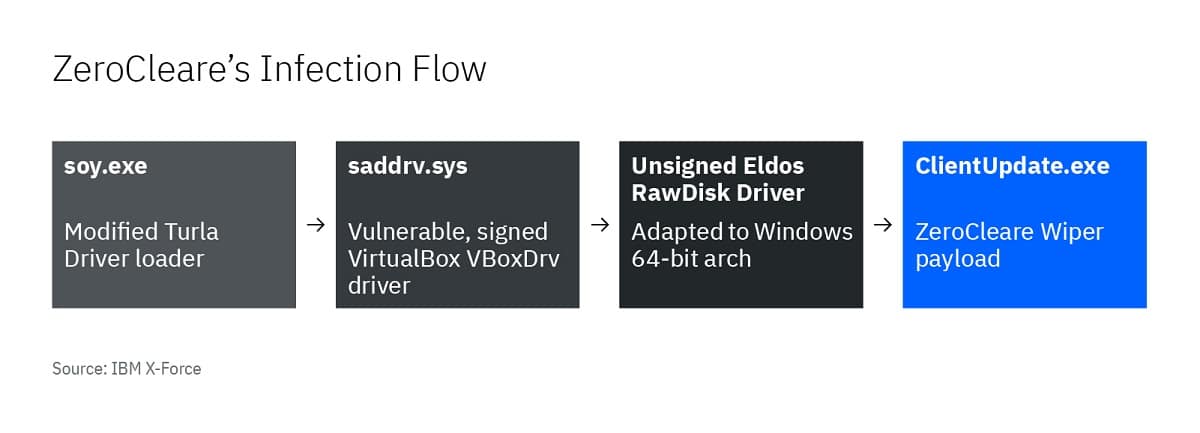
This driver is used to load a vulnerable version of the VirtualBox driver , which attackers exploit to load the EldoS RawDisk driver. RawDisk is a legitimate utility used to interact with files and partitions, and was also used by the Shamoon attackers to access the MBR.
To gain access to the core of the device, ZeroCleare uses an intentionally vulnerable driver and malicious PowerShell / Batch scripts to bypass Windows controls. By adding these tactics, ZeroCleare spread to numerous devices on the affected network, sowing the seeds of a destructive attack that could affect thousands of devices and cause outages that could take months to fully recover, "
Although many of the APT campaigns that researchers expose focus on cyber espionage, some of the same groups also carry out destructive operations. Historically, many of these operations have taken place in the Middle East and have targeted energy companies and production facilities, which are vital national assets.
Although researchers have not definitively identified any specific organization responsible for this malware, they initially suggested that APT33 was involved in the creation of ZeroClear.
And then later IBM claimed that APT33 and APT34 created ZeroCleare, but shortly after the document was released, the attribution changed to xHunt and APT34, and the researchers admitted they were not XNUMX percent certain.
According to researchers, ZeroClear attacks are not opportunistic and appear to be targeted operations against specific sectors and organizations.