
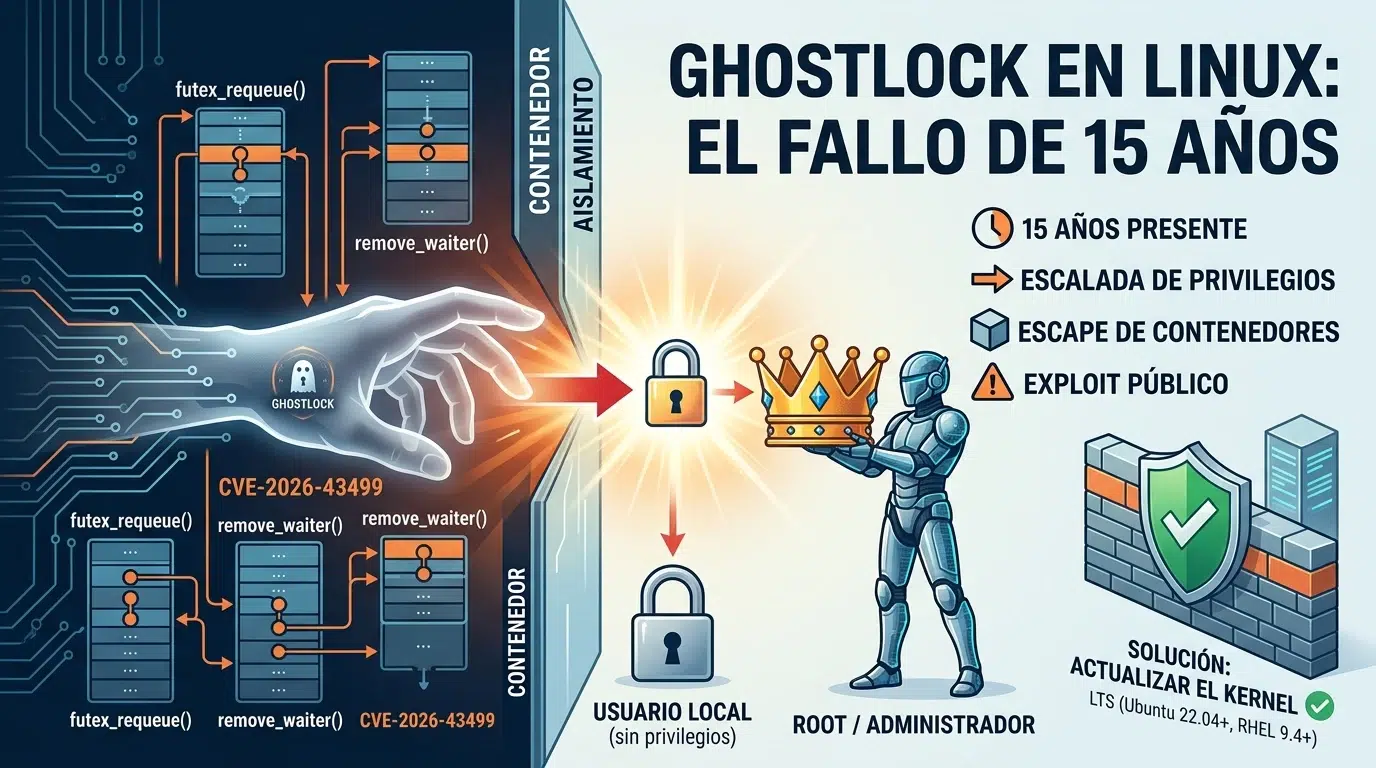
GhostLock It is the name given to a high-severity vulnerability discovered in the Linux kernel. Identified as CVE-2026-43499, affects the locking subsystem rtmutex and can cause a condition of use-after-free In certain Futex operations with priority inheritance, a local, unprivileged attacker could exploit the vulnerability to elevate their privileges to root and, in certain scenarios, escape from a container to the host system.
The problem is particularly relevant because the vulnerable code has been present in Linux for years and is part of a feature used by the kernels of major distributions. The fix has already been released in the main kernel and has also been backported to maintained branches, but users must ensure that their distribution has installed a kernel that includes the patch. It is not enough to simply check the kernel version number, as distributions often incorporate security fixes through backports.
GhostLock is a vulnerability in the rtmutex subsystem
The origin of GhostLock lies in the Linux kernel's priority inheritance mutex management code, specifically in kernel/locking/rtmutex.cThese mechanisms are part of the infrastructure used to coordinate the execution of different threads and avoid priority problems in certain workloads.
The vulnerability is related to the function remove_waiter()Under certain circumstances, the code could clear the information associated with the wrong process while handling a futex wait. The result was that a pointer could end up pointing to a memory area on the kernel stack that had already been freed.
This condition constitutes a use-after-free vulnerability : the kernel retains a memory reference whose lifetime has expired and can subsequently attempt to use it as if it were still valid. When an attacker manages to control the conditions necessary to reuse that memory, the flaw can become a much more serious vulnerability than a simple system crash.
The flaw affects futex with priority inheritance
To exploit GhostLock, it is necessary to interact with the futex priority inheritance path. Futex is one of the fundamental primitives that Linux provides for synchronizing threads between user space and kernel, and it is used indirectly by numerous applications and libraries.
The problematic path comes into play with futex requeuing operations that use priority inheritance. In a specific deadlock scenario, the kernel has to undo part of the operation and remove a process from a wait structure. It is during this recovery that the incorrect behavior occurs. remove_waiter().
The error essentially consisted of the function using current when I should use the task associated with waiterThe patch that fixes the problem changes precisely this behavior to use waiter->task.
A local attacker could gain root privileges
The most significant consequence of GhostLock is the possibility of local privilege escalation . A user who already has an unprivileged account on a vulnerable system can attempt to trigger the race condition and subsequently exploit kernel memory corruption.
This means that GhostLock is not a vulnerability that can be exploited simply by sending a malicious webpage to a remote user. The attacker first needs the ability to execute code on the affected system. However, that requirement does not make the problem trivial in environments with multiple users or where untrusted software is allowed to run.
Red Hat classifies the issue as having a significant impact and notes that it could allow privilege escalation or a denial of service. The published rating for CVE-2026-43499 is CVSS 7.8, placing it in the high-severity vulnerability category.
GhostLock can also be dangerous in containers
One of the aspects that makes GhostLock particularly interesting is its potential impact on systems that use containers. The vulnerable code can be accessed from a process running inside a container, so an attacker who has managed to compromise a workload can attempt to exploit the vulnerability against the host kernel.
In the worst-case scenario, this could turn a seemingly local vulnerability into a container escape . The isolation provided by the container ultimately depends on the host system's kernel, so an exploitable flaw in the kernel can break through that boundary.
This is especially important on multi-tenant servers, container platforms, continuous integration servers, and other infrastructures where code from different users or applications shares the same kernel. Red Hat and other security advisories recommend paying particular attention to these environments.
GhostLock had been in the kernel for years.
One of the most striking features of GhostLock is the age of the code containing the bug. The problem was introduced with a change made in Linux 2.6.39 , released in 2011, and remained in the code for approximately fifteen years before being fixed.
The flaw doesn't mean that all Linux installations from those years were actively exploited for that entire period. What it demonstrates is that a piece of code used for a long time can contain subtle bugs that only appear when certain synchronization conditions are met.
These types of vulnerabilities are especially difficult to detect because they don't depend on a simple operation like accessing a file or sending a network request. In this case, multiple threads, futex, priority inheritance, and a deadlock recovery path are involved.
Linux 7.1 already includes the fix
Correction of CVE-2026-43499 It arrived in the main kernel as part of Linux 7.1The change, identified by the commit 3bfdc63936dd, modifies remove_waiter() to use the task belonging to the item being removed instead of the currently running task.
The fix has also been rolled back to various stable branches of Linux. Therefore, it is not necessary to use Linux 7.1 or later to be protected. Patched versions exist in the LTS branches, including 6.18, 6.12, 6.6, 6.1, 5.15, and 5.10.
In other words, a system with an older kernel can be fully protected if its distribution has correctly implemented the back portFor this reason, only check the number it returns uname -r It may not be sufficient to determine the security status in distributions that maintain their own kernels.
The distributions have had to apply their own patches
Upstream patches don't necessarily reach users at the same time they're published on kernel.org. Linux distributions maintain their own kernel packages and typically incorporate security fixes into the branches they support.
For example, AlmaLinux released patched kernels for its versions 8, 9, and 10 shortly after the GhostLock vulnerability was disclosed. The distribution specified particular versions of its kernel packages containing the patch and recommended updating and rebooting the system to load the new kernel.
The situation is similar in other enterprise and community distributions. Therefore, the general recommendation is to use the official update channels for each distribution and check their respective security advisories, rather than assuming that a particular kernel is vulnerable or secure solely based on its base version.
There is no simple mitigation that can replace the patch.
Another important aspect of GhostLock is that there is no easy way to disable the vulnerable functionality without updating the kernel. The problem lies in generic code within the locking subsystem and in a futex route that is part of the kernel's normal capabilities.
Therefore, disabling certain namespace mechanisms or applying standard process containment restrictions is not equivalent to patching. Specifically, available information on GhostLock indicates that it does not rely on unprivileged user namespaces , so hardening this feature does not eliminate the vulnerability.
On servers where immediate updates are not possible, restricting access for untrusted users can serve as a defense-in-depth measure, but it does not eliminate the vulnerability. The real solution is to run a kernel containing the patch.
How to check if the kernel is up to date
Users can check the currently running kernel version with the command uname -rHowever, to determine if GhostLock It is corrected; you need to compare that result with the security status published by the distribution used.
In the upstream kernel, the fix has been present since Linux 7.1. In maintained branches, there are earlier versions that also include the patch, but the exact numbers vary depending on the branch and distribution. For example, vulnerability tracking identifies Linux 6.18.27, 6.12.86, 6.6.140, and 6.1.175 as patched upstream versions, among others.
Therefore, if the computer uses Ubuntu, Debian, Fedora, Arch Linux, RHEL, AlmaLinux, or any other distribution, it is appropriate to install the latest security updates available for that distribution and reboot if the kernel has been updated.
GhostLock demonstrates the importance of keeping the kernel up to date
GhostLock is a good example of how a vulnerability can remain for years in an extremely complex part of the Linux kernel without its impact being apparent until someone finds a way to reach the problematic path. In this case, a seemingly minor error in the handling of a process that waits for a mutex can end up providing a way to corrupt kernel memory.
The problem is especially relevant on multi-user servers and container platforms, where an attacker can have an environment from which to execute code without initially having privileges on the host system. The possibility of gaining root privileges or escaping the container significantly increases the importance of applying the patch.
The good news is that GhostLock has already been fixed in the main Linux kernel, and the fixes have been backported to maintained branches . Users don't need to switch distributions or install a development kernel; they just need to make sure their distribution has released the fixed kernel package and that their system is running it.